GRC
A risk register, a control framework and an evidence routine that hold up when someone asks to see them.
- Risk assessments and treatment plans
- Policies, standards and control mapping
- Audit and assessment readiness
- Third-party and vendor risk
MidState Cyber gives mid-sized organizations senior security, compliance and technology leadership without a full-time executive hire. We build the program, run it alongside your team, and prepare you for the assessor, the customer questionnaire or the board.
Most clients start with one problem, an audit, a customer requirement or a question from the board, and end up needing the others. We work across all four so the answers fit together. Independent testing, covered next, gives you an outside check on all of it.
A risk register, a control framework and an evidence routine that hold up when someone asks to see them.
Practical hardening and monitoring for the cloud and productivity platforms your people actually use.
Clear rules for how AI is used, so the business can move faster without leaking data or creating liability.
An experienced CISO, CIO, CTO or CAIO on a standing cadence, accountable for outcomes and not only for advice.
The people who build and run your systems should not be the only ones grading them. We scan and test under a written scope, then report in plain terms to your leadership and to your IT team, in house or outsourced.
Exhaustive, repeatable scanning that shows what an attacker could see and what is quietly aging on your network.
Controlled testing that shows whether weaknesses can be chained into real access, and how far an intruder could get.
An outside check is more credible to your board, auditors, insurer and customers than a self-assessment, and it is a relief to a busy IT team.
Each package has a defined scope and a finished deliverable. We tailor it to your size, sector and the frameworks that apply to you.
A clear picture of where you stand against the framework or requirement you care about.
The policies, controls and evidence routines needed to meet a framework and keep meeting it.
A named CISO, CIO, CTO or CAIO working with your team on a regular schedule.
Visibility into the AI already in use and a governance model that lets you adopt more of it.
Vulnerability scanning and penetration testing, scoped in writing and reported for both leadership and IT.
Briefings and training
Executive briefings, staff security sessions and AI webinars, delivered live for your leadership team, your board or your whole organization.
Scope and fees are set after a conversation about your environment and goals, so we do not publish a rate card.
We take the seat, own the outcomes and report to your leadership the same way a full-time executive would.
Chief Information Security OfficerSecurity strategy, risk ownership, incident readiness and regulator or customer answers.
Chief Information OfficerIT operations, vendor management, budgets and the systems the business runs on.
Chief Technology OfficerArchitecture, platform choices and technical direction for the products and services you sell.
Chief AI OfficerAI strategy, governance, use-case selection and responsible rollout across the organization.
Learn the business, interview stakeholders, baseline risk and technology, and agree what success looks like.
Deliver the roadmap, fix the quick wins and put owners and budgets against the larger items.
Move to a steady rhythm with regular reviews, leadership reporting and a tracked backlog.
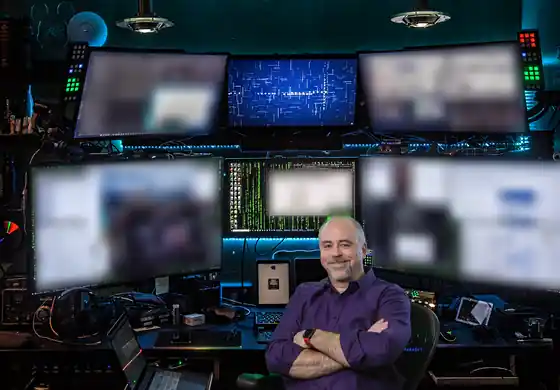
Chris has spent more than 40 years in IT and security, leading teams that protect organizations from small businesses to large corporations and local governments, across healthcare, finance, banking and non-profits.
He started out as a hacker and still looks at an environment the way an attacker would. We work alongside your internal or outsourced IT team, not around it, and fill whichever executive seat you are missing: CISO, CIO, CTO or CAIO.
He also helps leadership teams adopt AI without losing control of their data, and trains staff to use it safely.
Chris leads a small, growing team that is sharp in every service we offer. The goal is fewer surprises, clearer decisions and a team that understands why each control is there.
Select a framework to see what it is, who needs it and how we help. If yours is not listed, ask. Most requirements map to the same underlying controls.
We prepare and support you through assessments. Formal certification and attestation come from accredited third-party assessors and auditors.
A requirement from a customer, an upcoming audit, a gap in leadership, a question about AI. A short note is enough, and we reply with next steps.
Prefer to talk it through? Grab 30 minutes on the calendar.